Portfolio · Compliance and Risk
Cyber Incident Register
Logs cyber and technology incidents, rates their severity, works out which notices are triggered, and drafts them for review. Every notice is a draft and nothing is sent.
- Discipline
- Cyber and tech risk · Regulatory notices
- Status
- Concept demo. Not a client project. Runs on synthetic data only.
Request access to open it. The demo is labelled SYNTHETIC DEMO DATA and every notice is stamped DRAFT - NOT SENT.
The problem it solves
When an incident happens, the team has to judge how serious it is, decide who must be told, and write the notice quickly. Bank of Uganda's 2024 cyber and technology risk guidelines expect significant incidents to be reported within 24 hours, and the data protection law requires personal data breaches to be notified immediately.
How it works
01
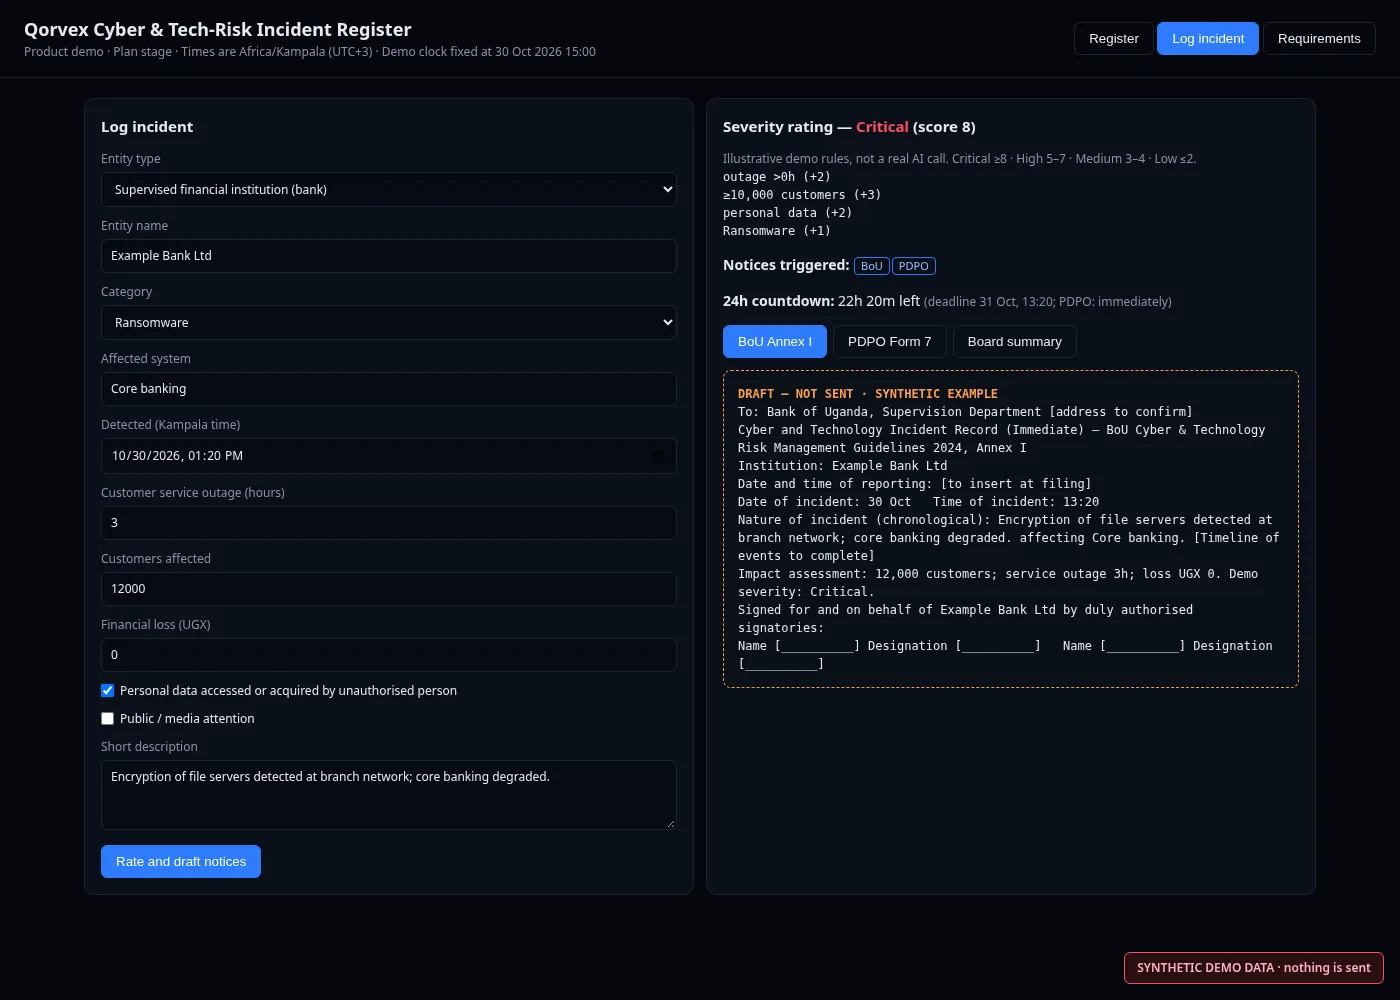
Log the incident: entity type, category, affected system, outage hours, customers affected, loss and whether personal data was accessed.
02
The register rates its severity using example scoring rules.
03
It works out which notices are triggered and shows the time left before the deadline.
04
It drafts each notice with the facts entered, for a person to check, sign and send.
Key features
Incident register
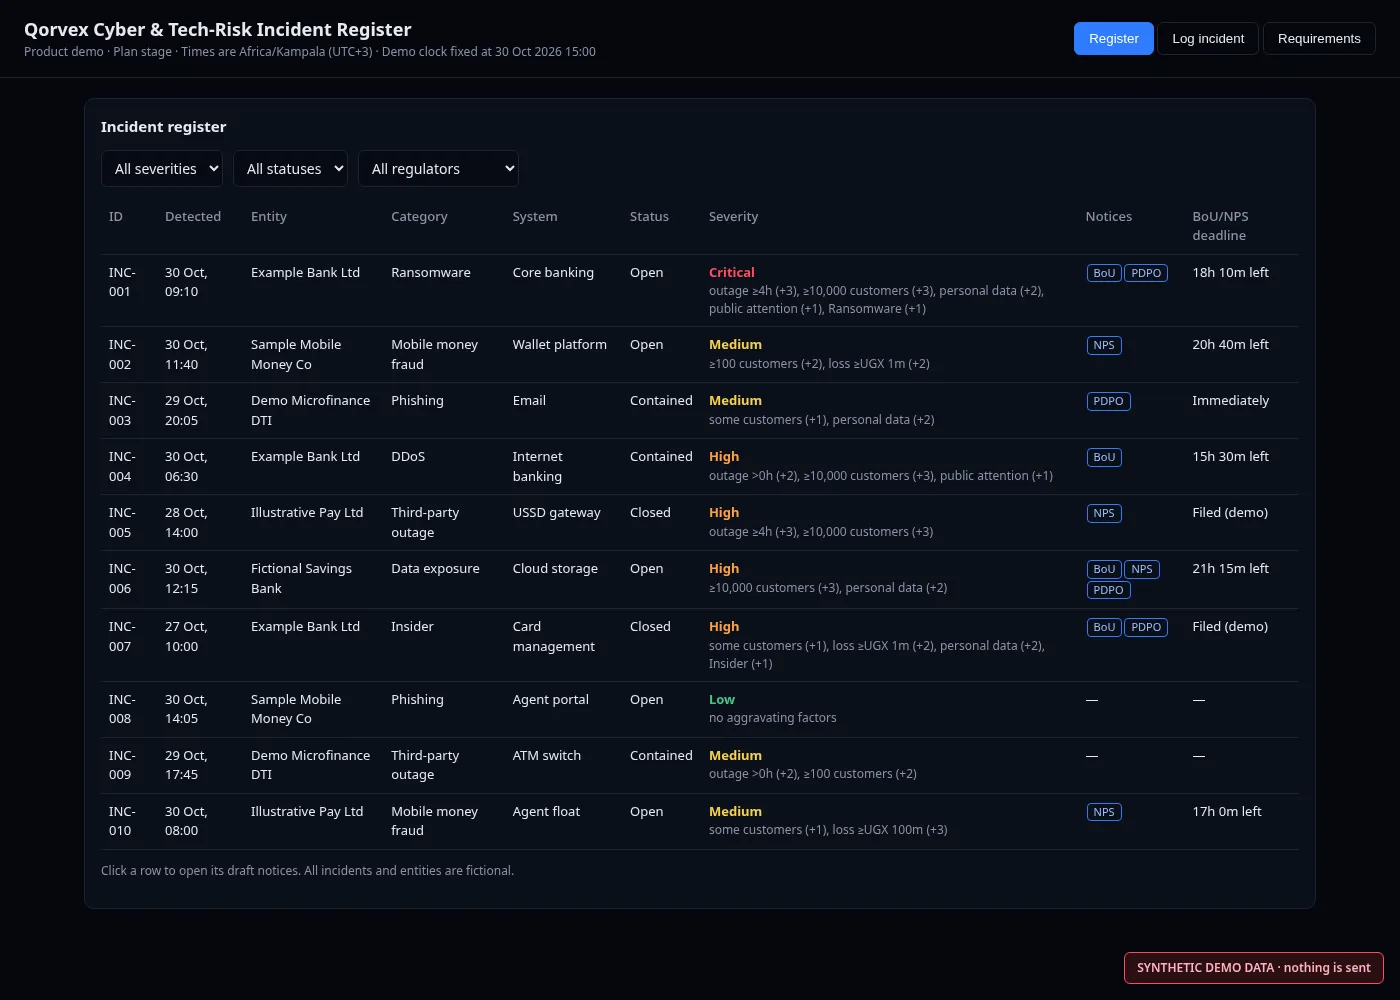
One list of incidents, filterable by severity, status and regulator, with each incident's notices and deadline.
Severity rating
Rates each incident from the details entered. In the demo the scoring rules are examples.
Drafted notices
Drafts the Bank of Uganda incident record and the data protection breach notice. Each is stamped DRAFT - NOT SENT.
Requirements table
Lists each rule with its deadline, who to notify, what to include and whether the source has been checked.
Who it is for
Supervised financial institutions such as banks, with e-money and mobile money issuers as a second group still to be confirmed.
What the demo shows
- The register, the log-incident form with its severity rating, and the drafted notices with a countdown.
What is real and what is example
Real
- Bank of Uganda Cyber and Technology Risk Management Guidelines 2024: significant, adverse incidents reported within 24 hours. Checked in the source.
- Data Protection and Privacy Act 2019 s.23: breaches notified to the Personal Data Protection Office immediately. Checked in the source.
Example
- All incidents and entities are fictional. The scoring rules and notice wording are examples.
- The demo also shows a mobile money (National Payment Systems) notice. That rule has not been confirmed in the official text yet, so treat it as unverified.
- Nothing is sent from the demo.
Screens from the demo
All incidents in these screens are fictional, and every notice is a draft.